Saturday, January 10, 2015

brute force with ncrack, hydra and medusa

nrack
wget http://nmap.org/ncrack/dist/ncrack-0.4ALPHA.tar.gz
./configure
make
make install
hydra
wget http://freeworld.thc.org/releases/hydra-6.3-src.tar.gz
./configure
make
make install
medusa
wget http://www.foofus.net/jmk/tools/medusa-2.0.tar.gz
./configure
make
make install
 ----------------------------------------
Medusa main page:
 http://foofus.net/goons/jmk/medusa/medusa.html

HOWTO : DirBuster on Ubuntu Desktop 12.04 LTS

HOWTO : DirBuster on Ubuntu Desktop 12.04 LTS

DirBuster is a multi threaded java application designed to brute force directories and files names on web/application servers.

Step 1 :

sudo -sH

cd /opt

wget "http://downloads.sourceforge.net/project/dirbuster/DirBuster%20%28jar%20%2B%20lists%29/1.0-RC1/DirBuster-1.0-RC1.tar.bz2?r=http%3A%2F%2Fsourceforge.net%2Fprojects%2Fdirbuster%2Ffiles%2FDirBuster%2520%2528jar%2520%252B%2520lists%2529%2F1.0-RC1%2F&ts=1370262745&use_mirror=nchc" -O DirBuster-1.0-RC1.tar.bz2

tar -xjvf DirBuster-1.0-RC1.tar.bz2

mv DirBuster-1.0-RC1 DirBuster

rm DirBuster-1.0-RC1.tar.bz2


Step 2 :

To run it.

sudo -sH

cd /opt/DirBuster

./DirBuster-1.0-RC1.sh


That's all! See you.

Wednesday, November 26, 2014

Cisco Catalyst 2960 Switch Configuration

Instructions on how to configure Cisco switch using Ubuntu:

Order:
Install minicom
Security
Banner
Host Name
Vlan IP
Default Gateway
Interface Setup

-------
Install & Configure Mini-Com to connect to switch.

Install mimicom
apt-get install minicom

identify serial com
dmesg | grep tty

start minicom configuration
sudo minicom -s

Default Setup:

serial port setup
change serial device ttyS0
change port speed to "C" 9600
Hardware flow control "no"

ESC to exit minicom
save setup as dfl
exit

---------------------------------------------------
https://www.youtube.com/watch?v=r88HmwQGd0s

To reset/ recover pwd:
power cycle switch while holding down mode button
this will bring up >

switch:

then

apply "flash init" command

switch:flash_init

then

load_helper

type dir at prompt

type "dir flash:" at prompt with the colon

type rename flash:config.text flash:config.old

#if the above fails do
switch: delete config.text

to confirm changes
type dir flash:

you will see config extension has changed to config.old

reboot switcht
type boot

select "no" on entering config dialog

type "enable" at prompt

the system will show
switch#

type "configure terminal"

system will return request for configuration commands.

Done!

------------------------------------------------------
Now to configure the switch:
http://www.youtube.com/watch?v=n_3CHv9bXdc

Secure the switch and console port:

Note:
After typing "configure terminal" the prompt
will be:

Switch(config)#

To change pwd type following at prompt:
"enable secret" (pwd goes here no brackets)

--------------------------------------------------------
To secure console port:
"line console 0"

The prompt will change to - Switch(config-line)
ie. Switch(config-line)#

Now we set pwd for console
password (pwd)

then type "login"

nothing will show at prompt

in case commands get broken up during input this will paste

them into next prompt
type "logging synchronous"

exect time out to 30 min 0 secs
type exec-timeout 30 0

do a ctrl-Z

the prompt will now be: Switch#


Now we configure vty ports:

type "configure terminal"

configure ports zero-four
type "line vty 0 4"

set synchronous logging and pwd (as done previously) @ prmpt

type:

password (pwd)

then

synchronous logging
type logging synchronous

this will return session to previous mode.
type exit

do ctrl Z if not at Switch# prmpt

to see what's written to RAM
type show-running config

observer enable secret is md5 hashed pwd

but there is a message stating no service password-encryption

enable srvc pwd encryption:
@prompt type:
"configure terminal"
 then
"service password-encryption"

ctrl Z

show running-config

service-password encryption will be enabled now.

**Security for device is now enabled


Save progress by typing at prompt:
"copy running-config startup-config"

-----------------------------------------------------------
Banner & Host Name:

enter global config mode:
Switch# "configure-terminal"

Switch# "banner motd" [ (message of the day)
then
*************************************

UNAUTHORIZED ACCESS IS PROHIBITED!!!

**************************************[

- the bracket "[" is necessary to initiate and terminate the
message entry. (it will not show in the msg)


change hostname
Switch(config)#HOSTname sw1

prmpt changes to
sw1(config)

do ctrl Z

type "copy running-config startup-config"
[OK] will be shown

DONE!

-------------------------------------------------------------
- VLAN CONFIG:

this will show port configuration
sw1#show ip interface brief

enter config mode
"configure terminal"

tell which interface to config
type "interface vlan1"

config interface ip and subnet
type #ip address 192.168.1.X 255.255.255.0

turn on interface
type "no shutdown"

ctlZ

confirm status UP
"show ip interface brief"

-------------
-Default GW

sw1#configure terminal
sw1#(config)
so
sw1(config)#ip default-gateway 192.168.1.1

ctl Z

type "copy running-config startup-config"

-------------
Interface setup - configure fast ethernet ports:

sw1>configure terminal

for a single port:
sw1#>interface fastEthernet 0/1

for the entire range:
interface range fastEthernet 0/1 -24

-------------
Save changes:
copy running-config startup-config

Done!


Thursday, November 6, 2014

W3af install on Ubuntu 14.04

Running apt-get install didn't work so here is what I did.

sudo apt-get install git

Install Python installer (pip)

sudo apt-get install python-pip python-dev build-essential

sudo pip install --upgrade pip

sudo pip install --upgrade virtualenv


If you don't have scapy on the system:

apt-get install scapy - install necessary libs.

Install these dependencies:


sudo apt-get install python-svn
sudo pip install pybloomfiltermmap

sudo apt-get install graphviz
sudo apt-get install libgraphviz-dev
sudo apt-get install libgraphviz
sudo apt-get install python-gtk2
sudo apt-get install python-gtksourceview2
sudo apt-get install python-scapy


All this needs to be installed as well.

  sudo apt-get install python2.7
  sudo pip install fpconst
  sudo pip install nltk
  sudo pip install SOAPpy
  sudo pip install pyPdf
  sudo apt-get install libxml2-dev
  sudo apt-get install libxslt-dev
  sudo pip install lxml
  sudo pip install pyopenssl


More libs:


 sudo apt-get install libssl-dev libsqlite3-dev libyaml-dev

Apparently the python version also needs modules:

clamd github git.util pybloomfilter esmre phply nltk chardet pdfminer concurrent.futures OpenSSL lxml scapy.config guess_language cluster msgpack ntlm Halberd darts.lib.utils xdot

After running the above follow the instructions and install clamav.


After installing any missing operating system packages, use pip to install the remaining modules:

    sudo pip install clamd==1.0.1 PyGithub==1.21.0 GitPython==0.3.2.RC1 pybloomfiltermmap==0.3.11 esmre==0.3.1 phply==0.9.1 nltk==2.0.4 chardet==2.1.1 pdfminer==20110515 futures==2.1.5 pyOpenSSL==0.13.1 lxml==2.3.2 scapy-real==2.2.0-dev guess-language==0.2 cluster==1.1.1b3 msgpack-python==0.2.4 python-ntlm==1.0.1 halberd==0.2.4 darts.util.lru==0.5 xdot==0.6


Install & Launch:

git clone https://github.com/andresriancho/w3af.git
$ cd w3af
$ ./w3af_gui


Monday, November 3, 2014

FireFox as hacking platform.

This collection of addons is useful for pen testing engagements.

Information Gathering:
 Whois & geo-location :
  •   ShowIP - Shows IP of current page in status bar. Allows queriying custom services by IP and hostname by rt and lft click of mouse.
  •   Shazou - (shazoo) japanese for mapping. allows geolocation discovery
  •   HostIP.info Geolocation - Displays Geolocation using hostip.infodata data
  •   ActiveWhois - gets deatails about site ownwer and  it's host server.
  •   Bibirmer Toolbar - Some tweaking necessary. Includes Whois, DNS Report, Geolocation, Traceroute, Ping.

 Enumeration/ Fingerprinting:
  •    Header Spy - shows http headers on statusbar
  •    Header Monitor - displays responses of top level documents returned by web server 


Social Engineering:

   People Search & Public Record - perform public searches record lookups with this addon.


 Googling and Spidering:
  •    Advanced dork - used to spider or scan for hidden files on a site using google's advanced    operators.
  •    Spider Zilla - mirror utility based on httrack from httrack.com
  •    Vew Dependencies - adds tab that lists all files which were loade3d to show current page. Good for spidering.


Security Assesment / Code auditing:
 Editors:
  •      JSView - Allows view of open source on any web page.
  •    Cert Viewer Plus - adds options to view certificates
  •    Firebug - edit and debug css, html and javascript on the fly.
  •    XML Developer Toolbar - allows XML developers' tools from browser.


 Headers Manipulation:
  •    Header Monitor - displays http response header of top level document returned by web servers.
  •    RefControl - Control what gets sent as the http referrer on a per-site basis.   
  •   User Agent Switcher - allows switching of user      agent with button.


Cookies and Manipulation:
  •     Allcookies - Dumps ALL cookies to firefox standard cookies.txt , Session cookies included. 
  •     Cookie Swap - enables swapping of sets of         profiles of cookies while browsing.   
  •     httpOnly - Adds httpOnly cookie support to Firefox by encrypting cookies marked as httpOnly on the browser side.   
  •    Add n Edit Cookies - allows editing of sessions    and saved cookies.


 Security Auditing:
  •    HackBar - enables testing for SQLinjections, XSS    holes and site security. Helps developers secure    their code.
  •    Tamper Data - view and modidy http/https headers    and post parameters
  •    Chickenfoot - allows code manipulation on the fly
  •  Proxy/ Web Utils
  •    FoxyProxy - replaces ff's proxy management. offers    more features than Switch Proxy, ProxyButton,    QuickProxy, xyzroxy. ProxyTex etc
  •    SwitchProxy - anonymizer and allows changing proxy configurations
  •    POW (Plain Old WebServer) - Uses SJS (Server-side     JavaScript to run a server inside browser.  Includes security features to pwd protect user's site. Used to distribute files, create wikis, chat rooms and search engines using SJS.

 Malware Scanner:

  •    QArchive.org web files checker - allows checking  webfiles for malware    
  •    Dr.Web anti-virus checker - checks files and pages  pre download
  •    ClamWIN Antivirus Glue for Firefox - scans downloaded files

  Anti Spoof

   refspoof: overide URL referrer from sites


  Misc:

   Hacking for fun
  •     Greasemonkey: customize web pages with java script
  Encryption:
 

  •     Fire Encrypter: provides encryption/ decryption    and hashing from ff.   


Wifi Pentesting basics - Kali

Wifi pentesting:

There are a number of ways execute the following.  I like to have a lot of this scripted. Scripted tools are out there as well, 
Pwnstar is one of my favorites, look into it!!

Crack A WPA Wi-Fi Password With Aircrack
How to Hack Your Own Network and Beef Up Its Security with Kali Linux
Kali Linux comes with a whole suite of apps for cracking Wi-Fi networks, including Aircrack and Reaver — both of which we’ve mentioned before for cracking WEP and WPA passwords, respectively.
However, WEP passwords aren’t that popular anymore (because they’re so easy to crack), and Reaver only works if a network has WPS enabled. So today, we’re going take another look at Aircrack and use it to brute force our way into a WPA network (with the help of a password list).

Step One: Configure Your Wireless Card

How to Hack Your Own Network and Beef Up Its Security with Kali Linux
First things first: disconnect from all wireless networks. Then open up terminal. In order to use Aircrack, you’ll need a wireless card that supports injections. Type this into the Terminal to make sure your card supports it:
airmon-ng
This lists all the wireless cards that support this crack. If you card doesn’t support injections, it won’t show up here. Yours is likely listed under interface as wlan0, but it may depend on your machine.
Next, type in:
airmon-ng start wlan0
Replace wlan0 with your card’s interface address. You should get a message back saying that monitor mode was enabled.

Step Two: Monitor Your Network

How to Hack Your Own Network and Beef Up Its Security with Kali Linux
Next, you’re going to get a list of all the networks in your area and monitor yours.
Type in:
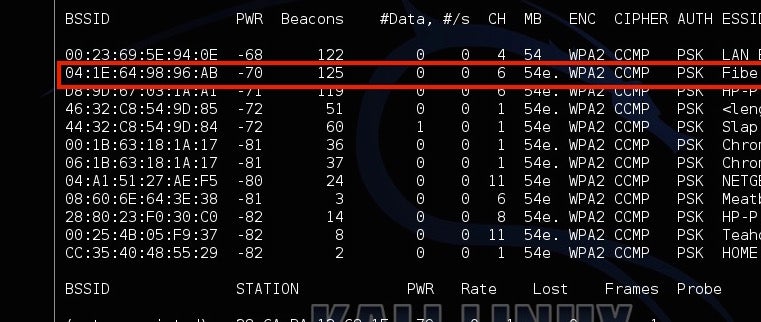
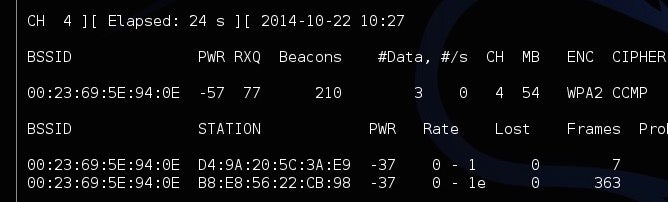
airodump-ng mon0
You’ll see all the networks in your area. Locate your network from the list, and copy the BSSID, while making a note of the channel it’s on. Type Ctrl+C to stop the process.
Next, type this in, replacing the information in parentheses with the information you gathered above:
airodump-ng -c (channel) --bssid (bssid) -w /root/Desktop/ (monitor interface)
It should read something like this:
airodump-ng -c 6 --bssid 04:1E:64:98:96:AB -w /root/Desktop/ mon0
Now, you’ll be monitoring your network. You should see four files pop up on the desktop. Don’t worry about those now; you’ll need one of them later. The next step is a bit of a waiting game, as you’ll be sitting around waiting for a device to connect to a network. In this case, just open up a device you own and connect to your Wi-Fi. You should see it pop up as a new station. Make a note of the station number, because you’ll need that in the next step.

Step Three: Capture A Handshake

How to Hack Your Own Network and Beef Up Its Security with Kali Linux
Now, you’re going to force a reconnect so you can capture the handshake between the computer and the router. Leave Airodump running and open up a new tab in Terminal. Then type in:
aireplay-ng -0 2 -a (router bssid) -c (client station number) mon0
It should look something like:
aireplay-ng -0 2 -a 04:1E:64:98:96:AB -c 54:4E:85:46:78:EA mon0
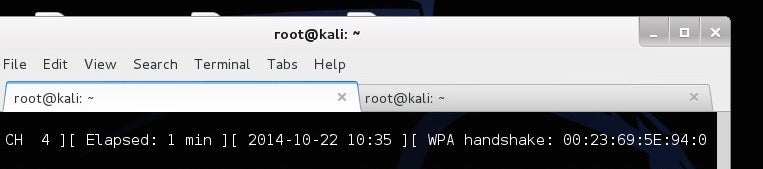
You’ll now see Aireplay send packets to your computer to force a reconnect. Hop back over to the Airodump tab and you’ll see a new number listed after WPA Handshake. If that’s there, you’ve successfully grabbed the handshake and you can start cracking the password.

Step Four: Crack The Password

How to Hack Your Own Network and Beef Up Its Security with Kali Linux
You now have the router’s password in encrypted form, but you still need to actually figure out what it is. To do this, you’ll use a password list to try and brute force your way into the network. You can find these lists online, but Kali Linux includes a few small lists to get you started in the /usr/share/wordlists directory, so we’ll just use one of those. To start cracking the password type this in:
aircrack-ng -a2 -b (router bssid) -w (path to wordlist) /Root/Desktop/*.cap
So, continuing with our above example and using one of the built-in wordlists, it should read something like:
aircrack-ng -a2 -b 04:1E:64:98:96:AB -w /usr/share/wordlists/fern-wifi/common.txt /Root/Desktop/*.cap
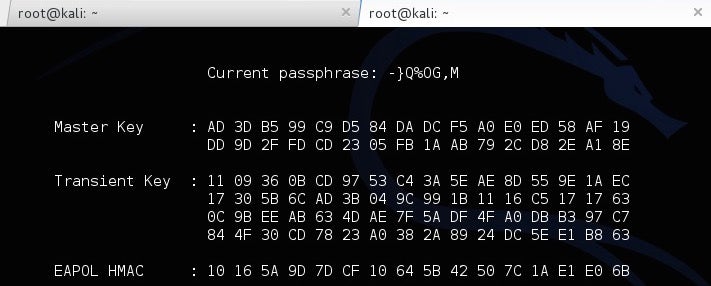
Now, Aircrack will try all of those passwords to see if one fits. If it does, you’ll get a message saying the key was found with the password. If not, give another one of the password lists a try until you find one that works. The bigger the password list, the longer this process will take, but the greater chance you have of succeeding.

How To Use This Information To Stay Safe

So, you just brute forced your way into your own network. Depending on how good your password is, it either took you five minutes or five hours. If your password is something simple, like “password123″, then chances are one of the smaller wordlists was able to crack it pretty quickly. If it was more complicated, it probably took a long time or never surfaced the password at all (if so: good for you!).
The best protection here is a good, strong password on your router. The longer, weirder and more complex it is, the better. Likewise, make sure you’re using the WPA2 security protocol and you don’t have WPS enabled.

Create A Fake Network With Airbase

How to Hack Your Own Network and Beef Up Its Security with Kali Linux
Next up, let’s take a look at how you can spoof a network address to trick people into signing into the wrong network so you can watch what they’re doing. Hackers might do this so you sign into the fake network thinking it’s your real one, then performing a man-in-the-middle attack (more on that in the next section) to gather information about you from your traffic. This is amazingly easy to do with a tool in Kali Linux called Airbase.
Essentially, you’ll turn your Wi-Fi adaptor on Kali Linux into an access point with the same name as another network. In order to do this, you’ll follow the same line of research as you did above, but the ending’s a bit different.

Step One: Configure Your Wireless Card

Just like last time, you need to set up your wireless card to monitor traffic. Open up Terminal and type:
airmon-ng
This lists all the wireless cards that support this crack. Yours is likely listed under interface as wlan0.
Next, type in:
airmon-ng start wlan0
Now you’re in monitor mode. It’s time to find the network you want to spoof.

Step Two: Find A Wi-Fi Network To Spoof

How to Hack Your Own Network and Beef Up Its Security with Kali Linux
In order to spoof a router, you’ll need some information about it. So, type in:
airodump-ng mon0
You’ll see all the networks in your area. Locate your network from the list and copy the BSSID, while making a note of its name and the channel it’s on. This is the router you’re going to spoof. Type Ctrl+C to stop the process.

Step Three: Create A Fake Network

How to Hack Your Own Network and Beef Up Its Security with Kali Linux
Now, you’re going to create the fake network with Airbase. Type this in, replacing the information you gathered in the last step for the parenthesis:
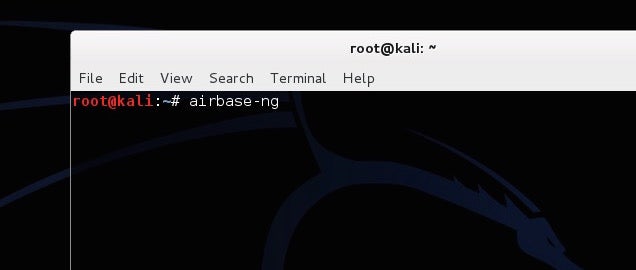
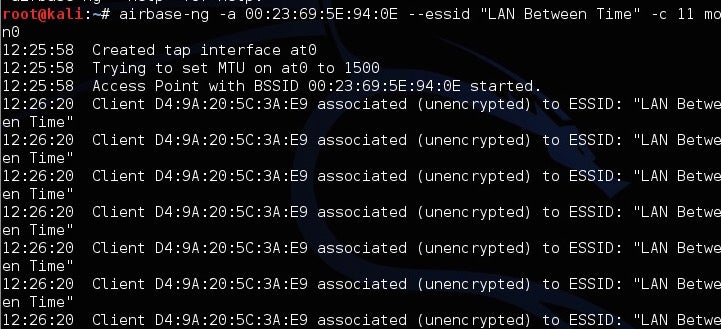
airbase-ng -a (router BSSID) --essid "(network name)" -c (channel) mon0
For example, it should read something like:
airbase-ng -a 04:1E:64:98:96:AB --essid "MyNetwork" -c 11 mon0
That’s it. You’ve now spoofed the router and created a clone with the same name, channel and SSID number so it’s indistinguishable from the original. Unfortunately, the computers on that network will always connect to the most powerful router with that name automatically, so you need to turn up the power of your fake network. Type in:
iwconfig wlan0 txpower 27
This bumps up the power of your fake network to the maximum accepted limit so hopefully next time they log in, they connect to you automatically. It shouldn’t do any damage to the card as long as you don’t go higher than 27. Once they do, it will be just like you’re both on the same network. That means you can access whatever they’re doing pretty easily.

How to Use This Information To Stay Safe

A spoofed network is tough to detect, but you can usually spot it when network traffic is slow, or if it suddenly doesn’t require a password authentication. If you’re really paranoid someone is spoofing a router, you can turn off the ability to automatically connect to Wi-Fi, so you at least have time to look at the router you’re logging into.

Snoop Another Device’s Traffic With ARP Spoofing

How to Hack Your Own Network and Beef Up Its Security with Kali Linux
A man-in-the-middle attack is essentially eavesdropping on your network. Here, you’ll intercept network signals between a computer and a router without the computer realising it. We’ve shown you how to dopacket sniffing for that purpose; today we’ll use ARP spoofing to gather this information. Both sniffing and spoofing are about listening in on conversations, but they work a little differently. Sniffing captures traffic by monitoring a network, spoofing pretends to be that network. These types of attacks are often used to grab passwords, images and almost anything else you’re sending over your network.

Step One: Turn On Packet Forwarding

First things first, you need to make your Kali Linux machine forward any traffic it gets so the target computer can still access the internet. Type this into the command line:
echo 1 > /proc/sys/net/ipv4/ip_forward
This will ensure all information is forwarded after it’s intercepted. That way, the internet and any other communications between the router and the target computer will continue to work.

Step Two: Turn On ARP Spoofing

How to Hack Your Own Network and Beef Up Its Security with Kali Linux
Now you need to turn on ARP spoofing. This tricks the computer and the router into thinking that your Wi-Fi adaptor is a bridge. When you successfully spoof, you can monitor all traffic between the devices. You’ll do this twice so you can capture traffic going to your computer from the router and from your computer to the router.
To capture traffic from your router type this in, replacing the parenthesis with your network’s information:
arpspoof -i wlan0 -t (router address) (target computer address)
You’ll see a bunch of number outputting showing that it’s running. Leave that running, then open another tab in Terminal and do the reverse:
arpspoof -i wlan -t (target computer address) (router address)
Both lines should look something like this:
arpspoof -i wlan0 -t 192.168.1.1 192.168.1.105
arpspoof -i wlan0 -t 192.168.1.105 192.168.1.1
Now, all the traffic between those two machines is being collected in Kali Linux. There are a lot of tools to actually capture this information; we’ll take a look at a couple of them here.
To track any URLs the computer visits, open up another Terminal tab and type in:
urlsnarf -i wlan0
This will display any web sites the computer visits.
If you’re more interested in images, you can capture any image traffic as well. Type in:
driftnet -i wlan0
A window will pop up and display any images they load and transfer over the network. Basically, if there’s any unencrypted information being sent between the router and the computer, you’ll see it happen.

How To Use This Information To Stay Safe

The best way to keep people from ARP spoofing your network is to secure your network with a strong password and make sure they’re not in there in the first place. That said, turning on a firewall on your machine helps as well. Also, make sure you’re always using HTTPS when it’s available. When HTTPS is on, an ARP spoofer won’t capture anything you’re doing. This is especially important when you’re on public Wi-Fi and can’t control a network’s security.

REF: http://www.lifehacker.com.au/2014/10/how-to-hack-your-own-network-and-beef-up-its-security-with-kali-linux/

Sunday, November 2, 2014

Network Ports

Common Network Ports:


Service Protocol Port TCP/UDP Tools
World Wide Web HTTP 80 TCP browsers
Name Resolution DNS 53 UDP nslookup
File Transfer FTP 21 TCP ftp
Secure Remote Shell SSH 22 TCP ssh
Simple Mail Transfer Protocol SMTP 25 TCP email clients
Post Office Protocol Version 3 POP3 110 TCP email clients
Secure Web HTTPS 443 TCP browsers
Remote Desktop
(microsoft-rdp)
RDP 3389 TCP rdesktop
File/Print Sharing
(microsoft-ds)
SMB 445 TCP map net-
work drive
Internet Relay Chat IRC 6667 TCP xchat


For the full list look here:

http://en.wikipedia.org/wiki/List_of_TCP_and_UDP_port_numbers